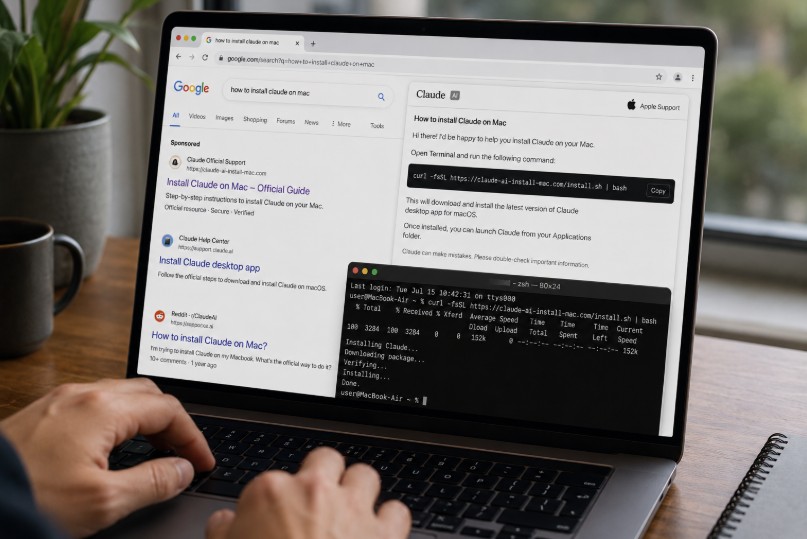
August 19, 2026: A search for help installing Claude on a Mac is being turned into an entry point for attackers, with a campaign using Google’s sponsored results and a fake support conversation to convince users to execute a malicious Terminal command.
The payload, identified as MacSync, is far more invasive than a conventional password stealer. Researchers at Huntress found that the malware can extract browser data and credentials, establish persistent remote access, capture screens and tamper with cryptocurrency wallet applications.
The campaign is particularly effective because the victim is not initially taken to an obviously malicious website. Instead, the attack borrows credibility from services users already recognize.
A sponsored Google result leads the target to a shared conversation hosted on Claude.ai, presented as an installation guide with an Apple Support-style appearance. The page then instructs the user to copy a command into macOS Terminal.
That command is the turning point. Once executed, it pulls down the malicious payload and starts a multi-stage infection process.
Google Ads, Fake Claude Support and a Terminal Command: How MacSync Infects Macs
Huntress researchers uncovered the campaign while investigating an incident involving a customer who had clicked the sponsored search result in July.
The attack relies on ClickFix-style social engineering. Rather than exploiting a software vulnerability, the operators persuade the victim to perform the critical action themselves.
The initial shell command launches a zsh-based loader, which decodes and executes the next stage. Huntress found that portions of the payload can change between victims, making traditional hash-based detection less useful.
For defenders, that shifts attention toward behavior. Unexpected curl downloads from Terminal, encoded data embedded in shell commands and suspicious command-line activity can provide stronger detection opportunities than simply looking for a known malware file.
The malware subsequently uses AppleScript and attempts to obtain high-level macOS permissions, including Full Disk Access. Granting those permissions can dramatically increase the amount of information available to the attacker.
The campaign’s objective is not limited to stealing a browser password. According to Huntress, MacSync can target browser cookies and saved credentials, Keychain information, account passwords, Telegram sessions, cloud credentials and SSH keys.
That creates a path from a compromised Mac into other services connected to it. The malware also deploys a remote-access component that establishes persistence through a macOS LaunchAgent. Once active, attackers can interact with the compromised system, execute commands and move files.
A separate signed helper seeks Screen Recording permission, potentially giving the operators the ability to capture what is displayed on the victim’s Mac.
For an attacker, that combination is considerably more valuable than a one-time credential dump. It creates an opportunity to maintain access while observing how the victim uses the machine.
Cryptocurrency wallets become the final target
The campaign becomes particularly concerning for cryptocurrency users. MacSync looks for numerous browser extensions and desktop applications associated with cryptocurrency wallets. Researchers found evidence of the malware copying and modifying selected applications.
The objective is to make the compromised software itself part of the attack. A victim may open what appears to be a legitimate wallet application only to encounter a fake error message asking for the wallet’s recovery phrase.
That request can be catastrophic. Unlike a conventional account password, a cryptocurrency recovery phrase generally cannot be reset after exposure. Whoever obtains the seed phrase may be able to gain control of the assets associated with it.
The tactic also illustrates why compromising trusted software can be more effective than simply sending a victim a conventional phishing page: the request appears inside an application the user already believes is legitimate.
The bigger lesson: search results are becoming part of the attack surface
The campaign highlights a broader problem for both consumers and security teams. Users have traditionally been taught to distrust suspicious attachments, unfamiliar websites and unsolicited emails. Search engines and mainstream AI services occupy a different psychological category: people expect them to help solve routine technical problems.
Attackers are exploiting that trust. The use of a legitimate Claude-hosted conversation does not make the instructions legitimate, just as appearing in a Google sponsored result does not mean a download is safe.
The most important warning sign in this campaign may therefore be the instruction itself: a website telling an ordinary user to paste an unfamiliar command into Terminal.
For individuals, software should be obtained through the vendor’s official channels, and commands copied from search results, forums or AI conversations should be independently verified before execution. Unexpected macOS permission requests should also be treated as a security decision, not a routine installation step.
For organizations, endpoint monitoring should focus on the behavior surrounding shell downloads, encoded commands, persistence mechanisms, new LaunchAgents and unusual permission requests.
And if a user has already executed the malicious command, simply deleting an installer is unlikely to be enough. Security teams should investigate persistence, browser sessions, cloud credentials, SSH keys and active authentication tokens. Cryptocurrency users should treat an exposed recovery phrase as compromised and move assets to a newly generated wallet where appropriate.
The campaign ultimately demonstrates how little an attacker may need from a victim.
Not a software exploit.
Not an attachment.
Not even a conventional phishing email.
Just a convincing answer to a search query—and one command pasted into Terminal.